Supplier questionnaires cannot see the subcontractor two vendors share
Published September 15, 2026·4 min read
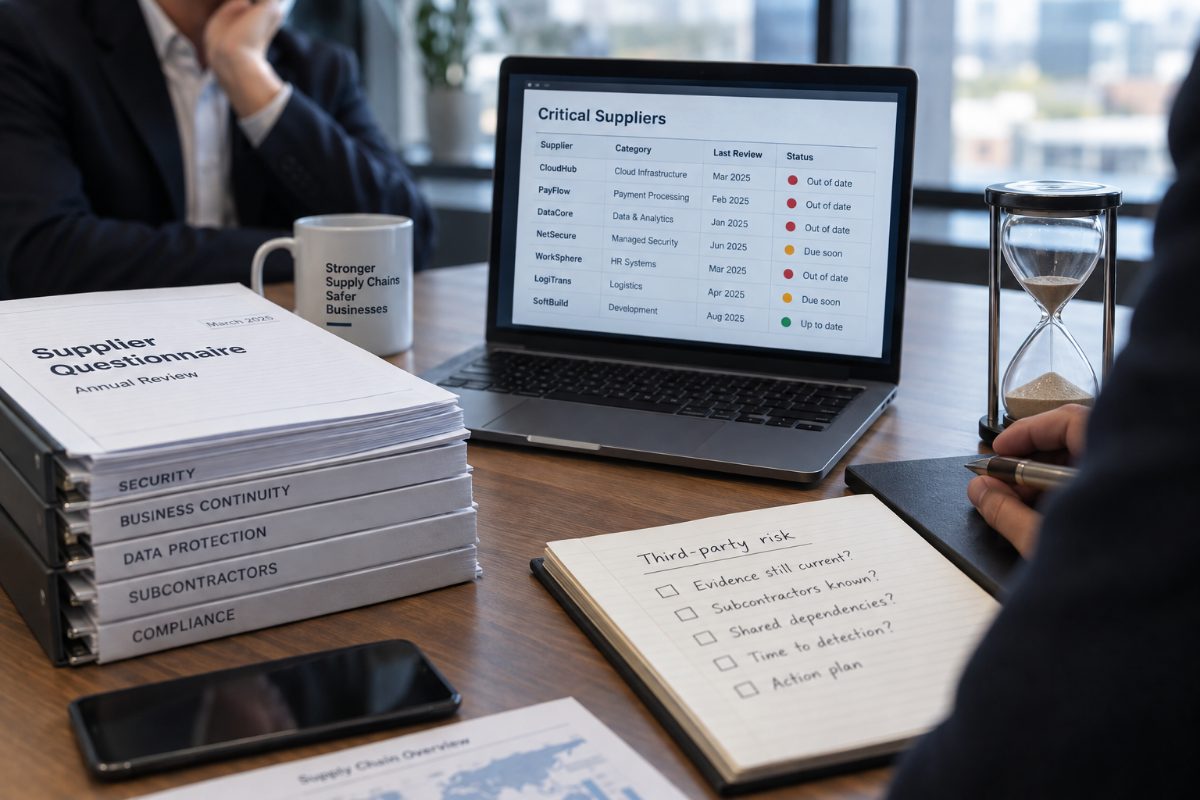
A supplier questionnaire that passed in June can be misleading by September without a single answer changing. The form was not wrong. The estate it described moved.
Alex Lee of Risk Ledger made a sharper version of that point in ComputerWeekly on 9 September 2026. Writing for channel partners, he argued that questionnaires answer a bilateral question: does this supplier patch systems, enforce multi-factor authentication and test disaster recovery? Those questions still matter. They just stop at the boundary of one contract.
The UK Cyber Security Breaches Survey, cited in the piece, puts the problem in numbers: only 15% of UK businesses review the cyber risks posed by their immediate suppliers, and 6% assess risks further down the chain. Even organisations that do run questionnaires are mostly checking the first link. They are not asking how many of those suppliers share a data centre, an identity provider or a payments processor.
The more useful reading is not that questionnaires go stale. It is that the questionnaire is structurally incapable of seeing the network. A single supplier can answer a form about its own patch cycle truthfully and still have no view of whether its subcontractors create a concentration risk with three of your other vendors.
The limitation no continuous monitoring fixes
At a firm where one person carries third-party risk alongside audit preparation and business continuity, the temptation is to buy more frequent assurance. Re-run the questionnaire quarterly. Add external attack surface monitoring. The article is candid that these tools have value. It is also clear about what they miss: none of them shows shared operational dependencies.
That distinction belongs in the board paper. Continuous monitoring tells you whether a given supplier's posture changed last month. It does not tell you that your primary and backup file-sharing providers both rely on the same subcontractor for encryption keys. That is a property of the graph, which no single node can reveal.
DORA and the UK's Critical Third Parties regime have pushed these questions from good practice into contractual clauses. Whether an organisation is directly in scope depends on entity type and regulator, but the direction travels through customer contracts regardless. A firm of a few hundred people may not be the named regulated entity. It is still the supplier answering due diligence questions from a bank or platform customer, and those questions are moving from does your supplier patch? toward show us the dependencies you cannot see.
This is where a managed third-party risk programme becomes operational. It means knowing which suppliers on the register share critical dependencies, and having someone chase the answer with each vendor instead of waiting for the next renewal.
The metric to take to the board
The most useful figure in the source comes from an exercise involving six financial institutions. Across them, nine suppliers supported at least half the participating organisations. Three were small businesses none of them had previously identified as strategically significant. That measures hidden concentration, and the method needs no special tooling.
Pick the five suppliers your organisation could not operate without for a week. For each, ask two questions. Who are the subcontractors that hold or can reach your data? And which of those subcontractors also appear in the chain of one of the other four? The first question a procurement owner can ask tomorrow. The second is where the concentration risk lives.
Most supplier registers answer the first with a form. Hardly any answer the second at all. That absence is what makes senior sign-off misleading. A board paper that reports a high return rate conceals the shared dependencies that could fail together. The better board metric is a count of shared dependencies among your critical suppliers, even if it starts at one.
You will not get that number from a questionnaire portal. You get it by treating the register as a graph and asking questions that cross contracts. A short conversation with an adviser about what that map would take is a reasonable step before the next annual cycle concludes. The source is aimed at channel partners, but the underlying shift applies to any organisation that spends a month chasing forms and still cannot describe its own supply chain.
If the suppliers that could halt your operations are businesses nobody on the board has heard of, who owns that concentration?
- supply chain risk
- third-party risk management
- supplier assurance
- shared dependencies
- dora
- questionnaires