A security roadmap now outlasts the CISO who signs it
Published September 15, 2026·4 min read
A board signs off a three-year security roadmap. Eighteen months later the CISO who wrote it resigns, and the board discovers that the roadmap's owner was the only person who understood which controls depended on which budget line. That is the pattern the 2026 CISO Report, published by Cybercrime Magazine in partnership with Sophos on 8 September, makes harder to ignore. The report collates multiple industry estimates that put average CISO tenure at 18 to 26 months.
Most readers will take it as another datapoint about burnout. There is plenty of that in the report: three quarters of security chiefs interested in changing jobs, almost all working extra hours, one in five working an extra 25 hours a week. But the more useful reading for a board is narrower. The churn is less important than the single point of failure it creates. When the security function is a person rather than a documented position, every resignation is also a data loss event.
A three-year plan with an eighteen-month author
The standard security improvement plan assumes a horizon longer than the average CISO now stays. A roadmap approved in January can be on its second or third owner before the final phase starts. Each handover resets informal knowledge: which risks were accepted, which suppliers were given conditional sign-off, which compensating controls were quietly compensating for something. In an organisation with a single security leader and no deputy, none of that has to be written down anywhere.
The problem is not simply that projects stall. A new CISO often re-baselines the programme, which consumes the first months of their tenure and discards decisions the previous one made. If tenure keeps running at two years, the organisation lives in a permanent state of transition. Compliance evidence accumulates in personal folders. The one person who can explain a finding to an auditor leaves, and the next audit starts from a weaker position.
What makes this acute in the mid-market is the absence of slack. There is no security team to absorb a departure. There is no deputy CISO, no threat-intelligence function, no established security steering committee. If the one accountable person leaves, the function leaves with them until a replacement is hired, and the hiring cycle for that role can run longer than the remaining patience of a regulator or a customer's security questionnaire.
The successor gap is where the risk actually sits
The report cites a Heidrick & Struggles survey finding that nearly half of surveyed CISOs did not have an adequate internal successor in place. That is the statistic boards should discuss, because it converts a people problem into a governance problem. A successor gap is not simply a resourcing gap; it is the absence of the documented, transferable knowledge that would let anyone step in.
For an organisation of a few hundred seats, the practical test is straightforward. If the person who currently owns security resigned this afternoon, what would still be true tomorrow morning? Would the board still know the top five risks? Would finance know which licences are in the renewals calendar? Would an auditor be able to see the same evidence trail? Most readers, if they are honest, know the answer is no.
The fix is not loyalty. Retention programmes are worth running, but they do not address what happens when a role changes hands for any reason: resignation, long illness, promotion, retirement, a hiring decision that does not work out. The institution needs the knowledge to stay when the person does not. That means written risk registers, documented decisions, a roadmap that names owners and dependencies rather than tasks, and reporting that a successor can pick up in the first week.
A test you can run before the resignation lands
There is a cheap way to find out where you stand. At the next leadership meeting, ask one question: If our security lead left tomorrow, who could run the next security committee meeting without a three-week briefing? If the answer is nobody, you have found the gap before an exit interview forces you to.
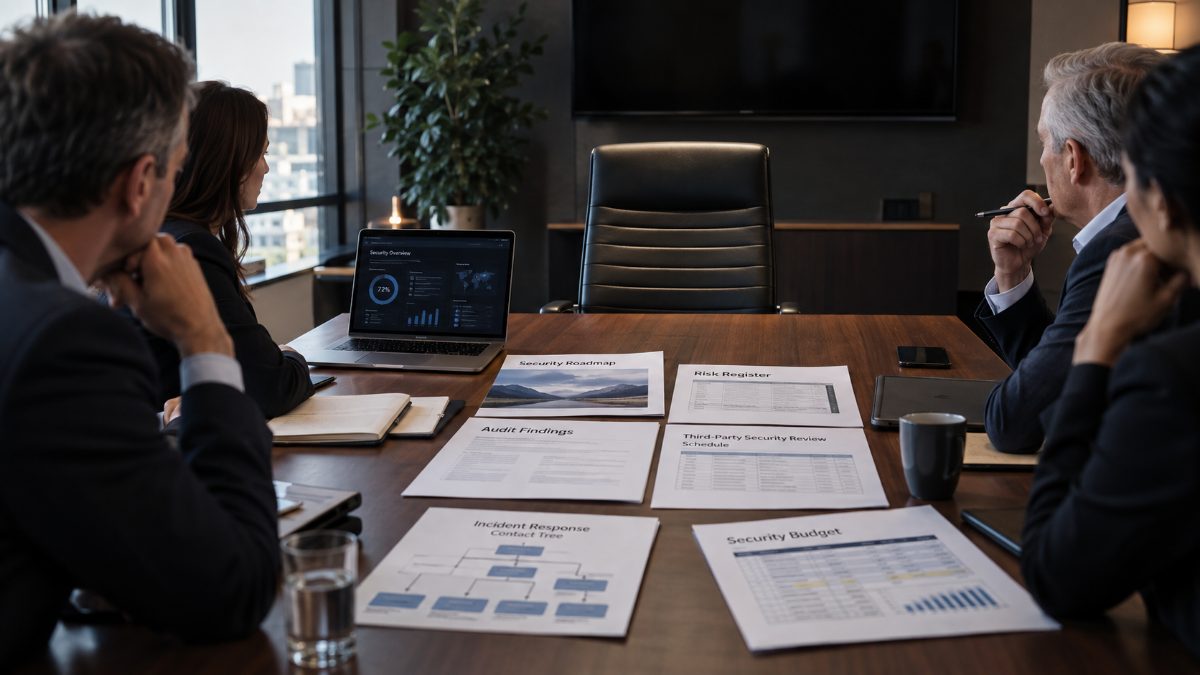
Then run a short document test. Ask the security lead to produce the five artefacts a successor would need in week one: the current risk register, the latest audit findings with owners, the supplier security schedule, the incident response call tree, and the roadmap with budget and dependencies. If any of these do not exist, they become this quarter's deliverable, not next year's.
A virtual CISO engagement is designed to make that handover explicit. The plan, the reporting and the decisions belong to the role rather than to the individual, so a change of person does not reset the programme. It is a structural answer to a structural problem. If you want a baseline before going further, the scored self-assessment will show where the gaps are most likely to sit.
The numbers in the report will probably look better in two years. The underlying condition will not. Security strategy in a mid-market organisation will continue to rest on one or two people unless the organisation deliberately builds the successor artefacts now.
- ciso turnover
- succession planning
- security leadership
- governance
- board reporting